Cybersecurity
Threats, regulation and the leaders responsible for resilience.
Companies House filing flaw leaves directors to check their own records
A WebFiling bug could let logged-in users view and change other companies’ details for five months. Companies House says no misuse is confirmed, but the government cannot yet say how many accounts were affected
Mid-market security teams are caught between SMB and enterprise tools
Intruder’s own survey of 502 UK and US security leaders finds confidence falling the closer respondents sit to the work, and cyber risk rarely reaching the board
How MSPs should prepare for the Cyber Security and Resilience Bill
Around 1,214 UK MSPs could be designated under the Bill and face 24-hour incident reporting. Matt Middleton-Leal, managing director at Qualys, sets out why continuous compliance and automation will be needed
Cybersecurity training still doesn’t stick, and that’s a leadership problem
Most cyber incidents start with a human decision under pressure, not a zero-day exploit. Phil Rowell, COO of Wizard IT Group, on turning people risk into operational resilience with blame-free leadership
Microsoft Copilot is changing how cybersecurity leaders think about risk
Phil Rowell, COO at Wizard Cyber, on how Microsoft Copilot is reshaping cyber risk judgment, leadership accountability and decision-making across the organization
Court of Appeal says firms must secure data hackers cannot identify
The ICO wins its appeal over the 2017–18 cyberattack on DSG Retail. The ruling settles which stolen data falls inside the security duty, whoever ends up holding it
Cyber Essentials needs the IT provider, not just the business owner
The government is urging small firms to ‘lock the door’ with Cyber Essentials. But many small businesses outsource security to an IT provider, and the campaign barely speaks to them
CrowdStrike’s Kurtz calls 2026 the breakout year for the agentic SOC
George Kurtz, CEO of CrowdStrike, says “the SIEMs of yesterday are being replaced” by AI agents, opening a services-led opportunity for partners in integration and managed detection and response
CrowdStrike CEO calls 2026 the ‘breakout year’ for agentic SOCs
CrowdStrike chief executive George Kurtz expects agentic security operations centers to break out in 2026. Uneven data quality, governance and skills mean the pace will vary widely across enterprises
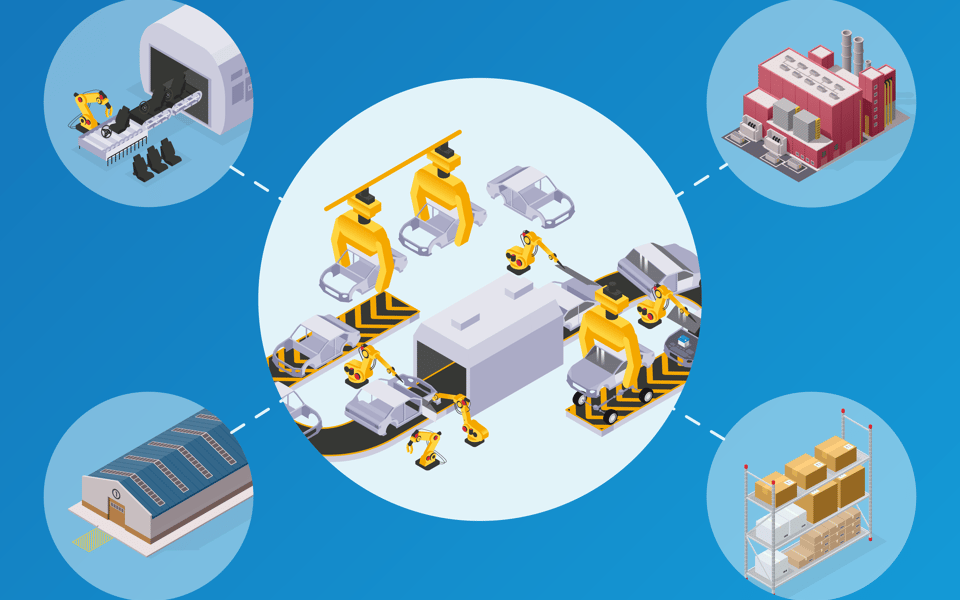
CFC insures SMEs against a cyberattack on a key customer
The specialist insurer’s new extension pays out when a customer hit by hackers cancels orders, a gap it says the Jaguar Land Rover attack laid bare across the carmaker’s supply chain
Whitehall’s cyber plan makes every supplier part of the audit
The Government Cyber Action Plan sets out how Whitehall will police cyber risk in its own estate. But its supplier clauses turn mid-sized contractors into part of the assurance chain