Cybersecurity
Threats, regulation and the leaders responsible for resilience.
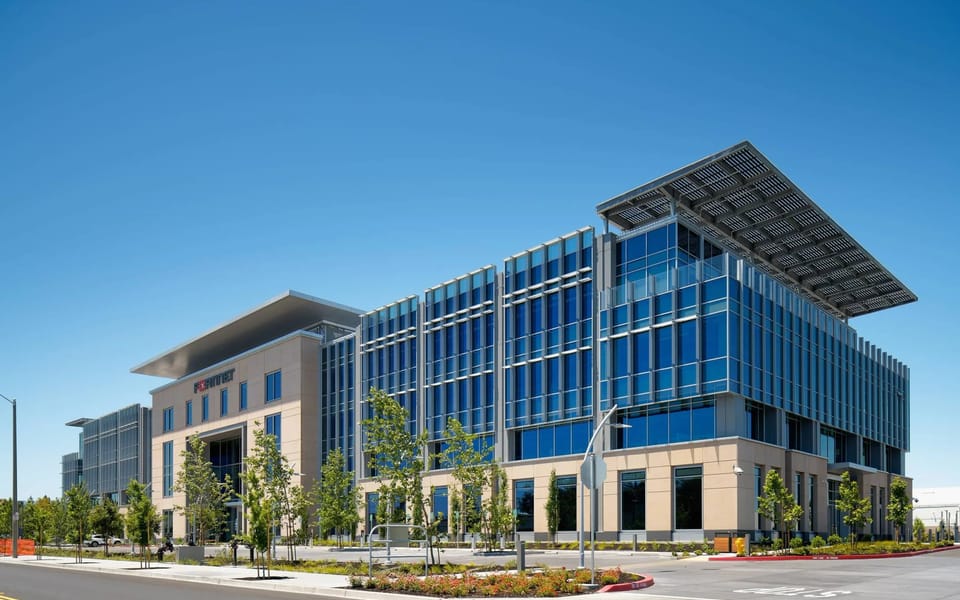
Fortinet warns of exploited FortiMail flaw with no fixed release out
Attackers are already using the critical bug to write files to email gateways. Until fixed releases arrive, mid-market firms depend on a workaround and on whoever runs their kit
ISACA finds European cyber teams understaffed as attacks rise
The professional body’s annual workforce survey shows attacks climbing while budgets and headcount lag. Fewer than one in three European organizations have rehearsed an AI-related incident
Barracuda bundles AI governance into SecureEdge for MSPs
AI Data Security arrives in October at no extra cost in SecureEdge Premium Access, handing partners a ready-made AI governance service but perhaps little room to charge for the tool itself
Double the CVEs: patching everything is no longer a security strategy
Google’s threat intelligence group says monthly vulnerability disclosures doubled between January and August. But only about one in 431 was seen exploited, and teams that still try to patch everything risk being slowest on the flaws that matter
PixelLeak: coding agents are publishing what security teams can’t see
AI coding agents at more than 300 organizations posted internal screenshots to public GitHub repositories, mostly under employees’ personal accounts. Nobody hacked them. They were left to decide where company data could go
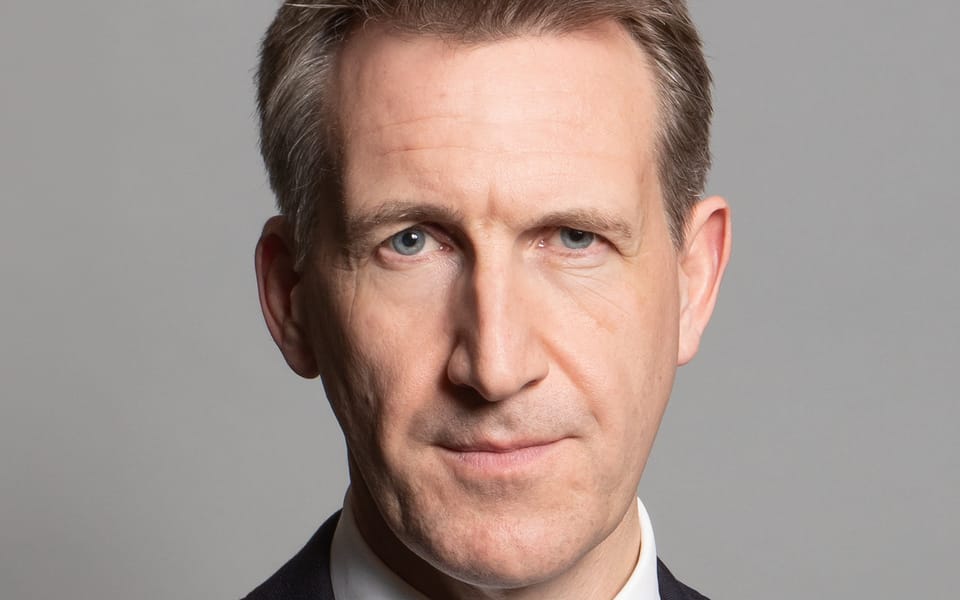
Don’t wait for the National Cyber Action Plan: the pledge sets the bar
Security minister Dan Jarvis said on 30 September that a National Cyber Action Plan covering the private sector is coming soon. Its central pillar, the Cyber Resilience Pledge, already sets out what the government wants from boards
Deepfake fraud: fix the approval chain before buying a detector
Pindrop’s survey of 250 US security leaders finds deepfake attacks costing some firms $1m or more from a single incident. Its answer is detection. For UK boards, the faster fix sits in payment, help-desk and executive approval rules
Only one in 10 sure of meeting 24-hour breach reporting, VinciWorks finds
A small poll by a compliance training firm suggests most organizations have never tested the escalation process the Cyber Security and Resilience Bill will demand of them
NCSC sets out the standard for assured red-team providers
The first Cyber Adversary Simulation scheme documents show what the NCSC will expect of commercial providers when the scheme opens in November, and give buyers a benchmark to hold them to
Agentforce flaws let a poisoned web lead leak CRM data over DNS
Salesforce fixed the Trusted URLs bypasses in August and has changed its Slack defaults, but the attack needed no login, no click and only the permissions the stock CRM subagent ships with
Kiteworks tells every customer to switch off over a zero-day warning
The secure file-transfer vendor asked customers to take self-managed systems offline for nine hours over the weekend, found and fixed a critical flaw during the window and lifted the advisory on 27 September