Cybersecurity
Threats, regulation and the leaders responsible for resilience.
Kiteworks tells every customer to switch off over a zero-day warning
The secure file-transfer vendor asked customers to take self-managed systems offline for nine hours over the weekend, found and fixed a critical flaw during the window and lifted the advisory on 27 September
Citrix patches eight NetScaler flaws as two zero-days are exploited
CISA has given US federal agencies until 30 September to act and the National Cyber Security Centre is telling UK defenders to isolate affected appliances, while some IT suppliers told customers to pull the plug
Cyber Essentials passes 61,000 certificates, mostly renewals
Government figures show certificate numbers up by a fifth in a year, but nearly three in four basic certificates went to organizations renewing rather than joining for the first time
Sophos survey says MSPs act as CISO for almost half their customers
In the security vendor’s own survey, MSPs say compliance shapes half of their customers’ security purchasing decisions. It arrives weeks before Sophos launches a service designed to bill for that work
IBM buys UK defense security consultancy Logiq Consulting
The consultancy, assured by the National Cyber Security Centre, brings Secure by Design work and a government data-sharing platform into IBM’s UK business. For partners chasing defense and government contracts, a big rival just got more specialist
UK education’s cyber gap is the patch queue, not the attack count
SonicWall’s own UK telemetry shows intrusion attempts on schools, colleges and universities climbing while ransomware stays rare. The numbers point governors to patching, not more monitoring
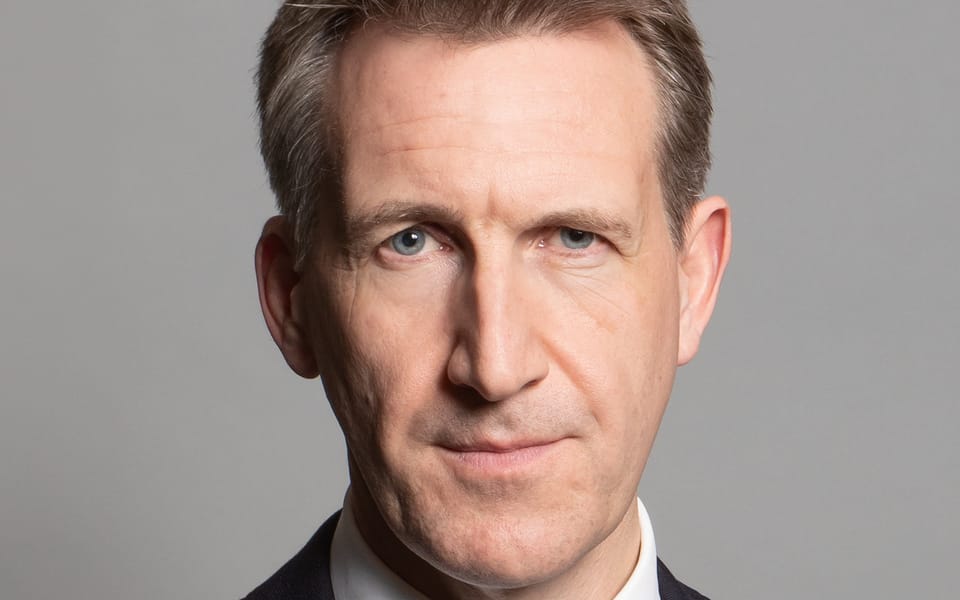
Whitehall’s Russia briefings must not stop at the boardroom door
Dan Jarvis will brief critical infrastructure chief executives on Russian cyberattacks, sabotage and disinformation. But the threat arrives through operational technology, remote access and suppliers, and only 15% of UK businesses review the risks their immediate suppliers pose
The Storm-3168 Azure attack is about credential hygiene, not agentic AI
Microsoft says JadePuffer, the actor it tracks as Storm-3168, hijacked two Azure service principals and deleted most of the storage accounts it targeted in about seven minutes. CISOs should dwell on a client secret posted in a public GitHub issue
AI writes the code now: the software bill of materials is the control
Intekhab Nazeer told Raconteur that AI is now writing, testing and deploying code, and bringing new risk with it. UK MSSPs should sell supply-chain assurance before the law makes customers ask for it
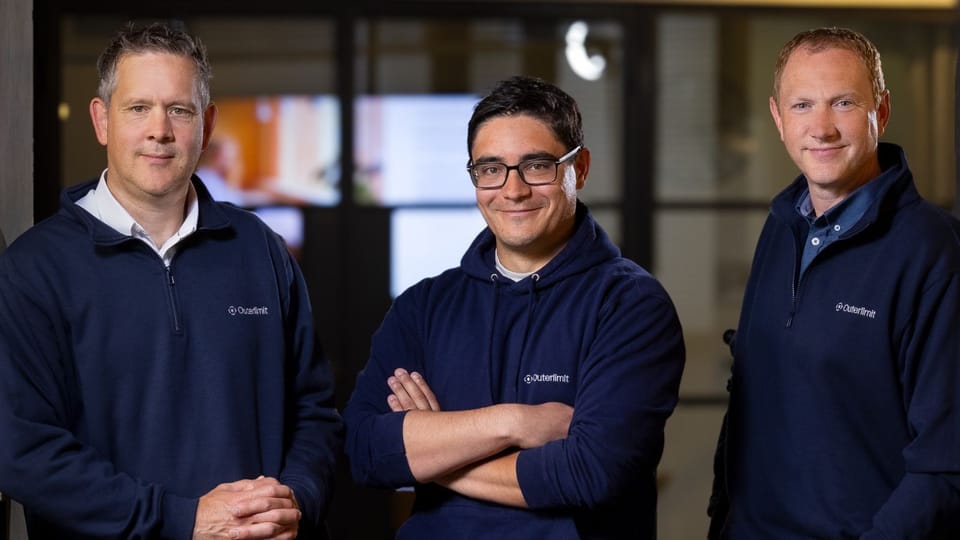
Egress founders return with $16m to police what AI agents do
Tony Pepper and Neil Larkins sold Egress to KnowBe4 in 2024. Their new London and New York startup, backed by AlbionVC, Evolution Equity and Crane, checks every tool call an agent makes before it runs
Nozomi’s independence promise is one partners should hold it to
George Todd told Raconteur that finance leaders should be doers first and that conventional wisdom can be completely wrong. UK partners should apply that test to Nozomi’s own promise of independence under Mitsubishi Electric
Microsoft and the Met dismantle EvilTokens, an AI phishing kit for hire
The Telegram-sold service charged $1,500 (£1,100) to join and $500 (£370) a month, sidestepped multifactor authentication on Microsoft 365 and used a chatbot to read stolen inboxes for payment fraud